nSIEM dev diary · First look ·
What nSIEM is for
Every Windows machine keeps a running record of what happens on it: who signed in, which services started, what PowerShell ran, what the built-in antivirus noticed. On one machine that record is useful. Across many, it is unreadable — unless something collects it into one place and makes it searchable.
That is nSIEM's job: a small agent on each machine sends its logs to a console you host yourself, where they can be searched together.
What the test was
A disposable virtual machine with the nSIEM agent installed, left to run normally. No attack and no special setup — just the logs an ordinary Windows machine produces, arriving in the console.
What it looks like
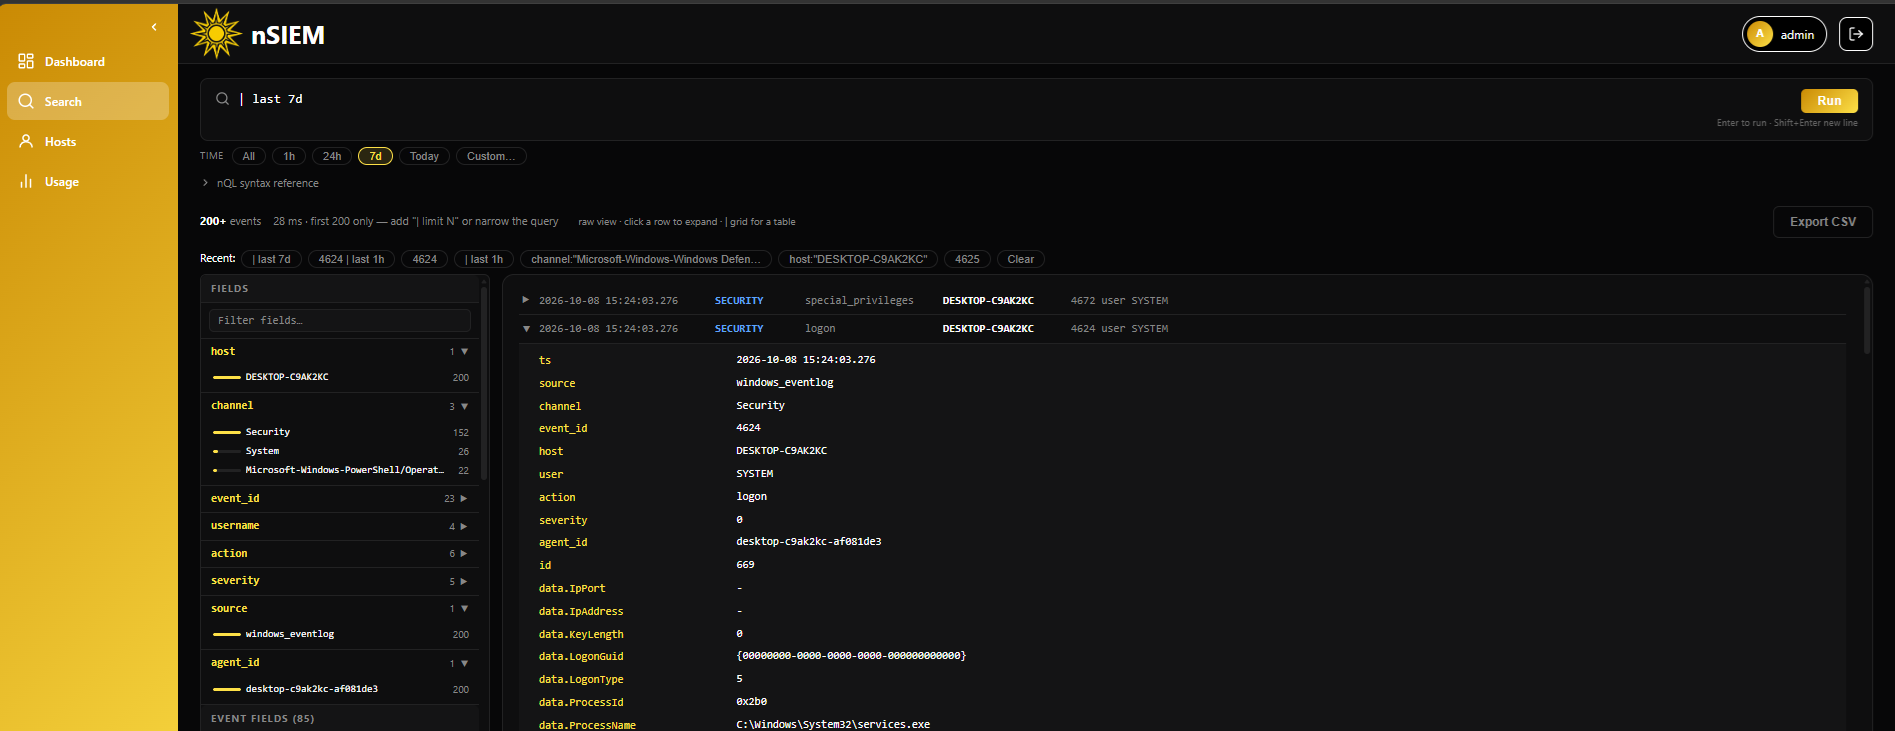
The lab machine's logs arrived from three sources — security, system and PowerShell — and one query brings them back together. The panel on the left counts what is in the results, so you can see at a glance which machine, which source and which kinds of event make up what you are looking at, and narrow down from there.
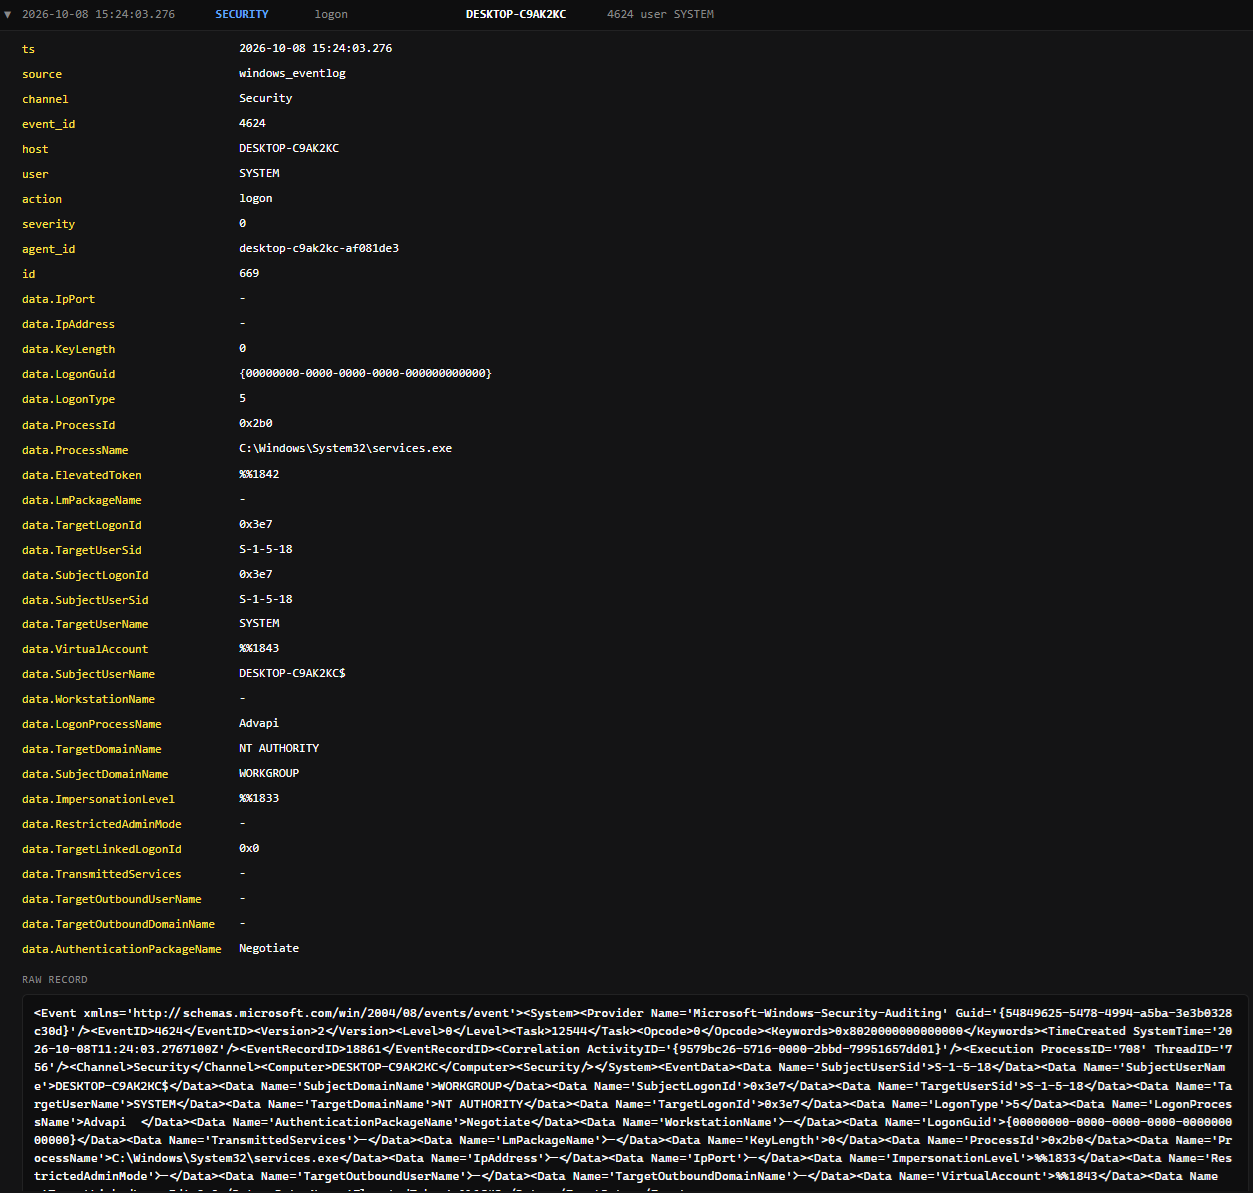
Each event is broken into named fields before it leaves the machine, so it can be searched by who, where and what — while the original record is kept underneath, untouched, for when the exact wording matters.
What it does not do yet
It collects and searches; it does not raise alerts yet. Turning these logs into detections is the next stage of the work, and it is not what this entry shows.
One machine, one lab. This is the first agent sending real data. Many machines, and the volume that comes with them, are still to be tested.
← All nSIEM entries